CrossClassify
AI-driven fraud detection for web and mobile apps. Continuous post-login monitoring that catches account takeover, bot attacks, and insider threats that WAF and MFA miss — live in under 48 hours, no rip-and-replace required.
What it does
Continuous 24/7 Monitoring
CrossClassify monitors every authenticated user session around the clock — not just at login. Threats that emerge mid-session, like session hijacking and privilege escalation, are detected in real time rather than caught after the damage is done.
Geo Analysis
Detects impossible travel, VPN abuse, and location anomalies that indicate compromised credentials or unauthorized access. Flags sessions originating from unexpected regions against each user's established patterns.
Behavior Analysis (AI)
Machine learning models build a behavioral baseline for each user — click patterns, navigation habits, timing, and interaction signatures. Deviations from the baseline trigger risk scoring, not noisy rule-based alerts.
Link Analysis
Identifies coordinated fraud rings and shared infrastructure across accounts. CrossClassify surfaces connections between seemingly unrelated accounts that share devices, IPs, fingerprints, or behavioral patterns — exposing organized attacks your per-account rules would miss.
Alerting & Notifications
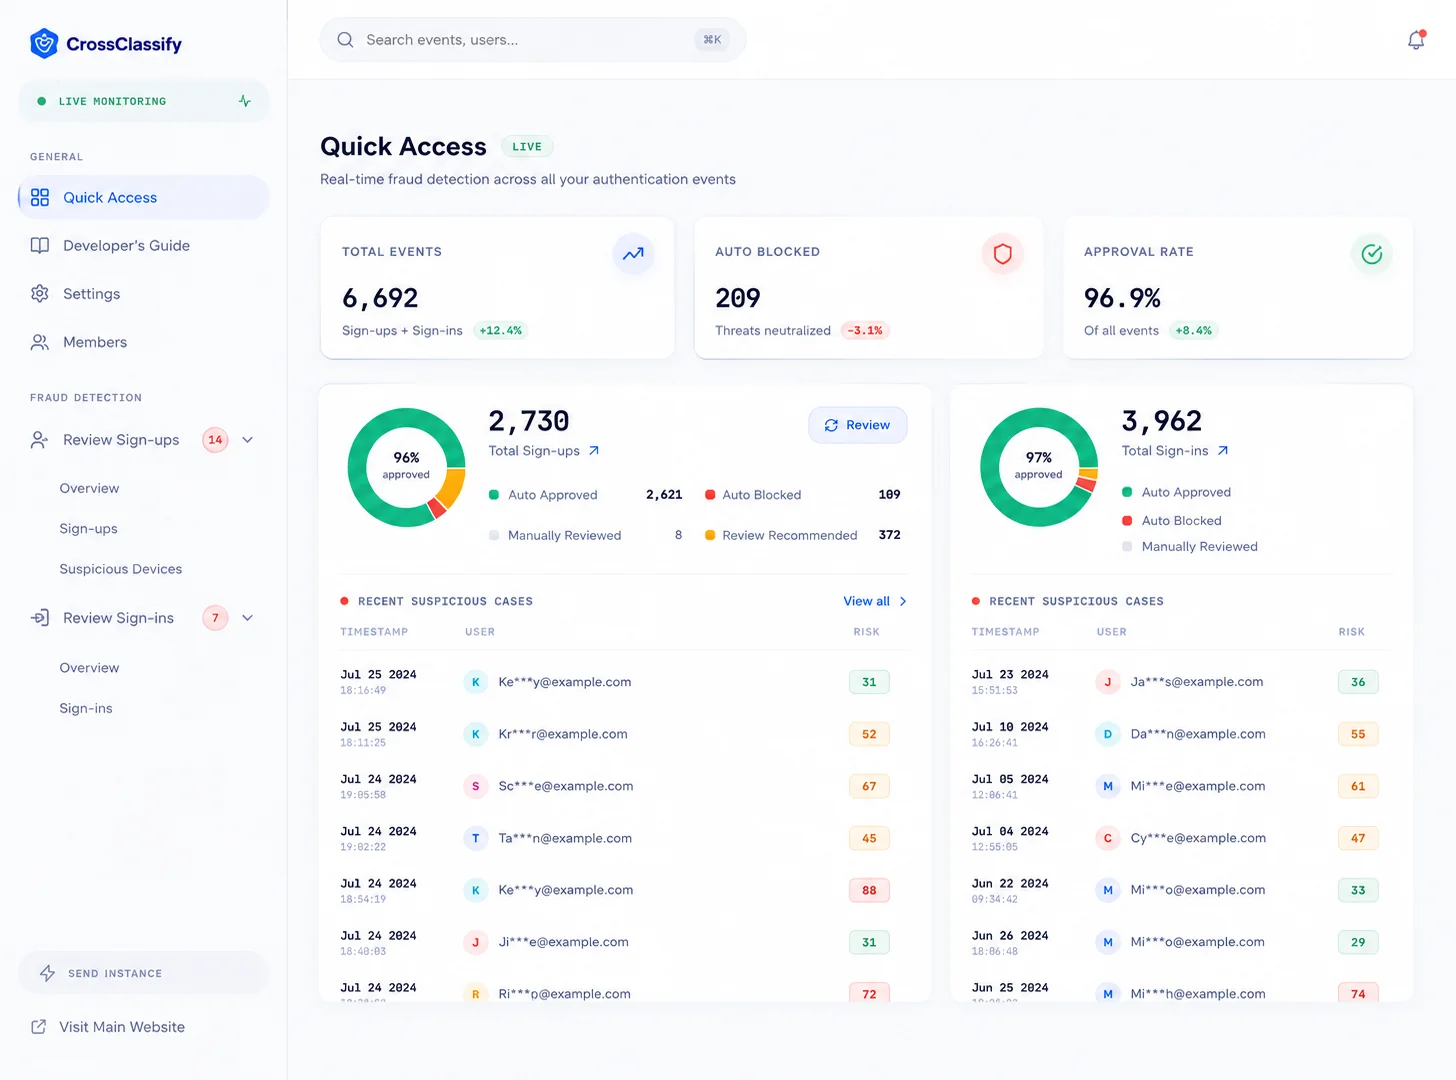
Risk events surface in a clear dashboard with priority scoring and full context. Configurable alert thresholds let security teams focus on high-confidence threats. Webhook integrations push alerts to Slack, PagerDuty, or your existing SIEM.
Seamless SDK Integration
Client-side SDK drops into any web or mobile app in a few lines of code. Server-side events API handles back-end signals. No infrastructure changes, no rip-and-replace — CrossClassify works alongside your existing auth stack, WAF, and MFA.
Threats it protects against
CrossClassify detects the attacks that slip past traditional perimeter defenses and authentication controls.
CrossClassify is GDPR-compliant and operates with data minimization principles. SOC 2 Type II certification is in progress. User behavioral data is processed for security purposes only and never sold or shared with third parties.
Who it's for
Web App Teams
Protect authenticated users from post-login threats without adding friction to legitimate sessions.
Mobile App Teams
Extend fraud detection to mobile sessions with the same SDK integration model used for web.
Fintech
Meet regulatory expectations for continuous transaction and session monitoring while reducing fraud losses.
Any Org with Post-Login Sessions
If your users authenticate and then do things, CrossClassify monitors what happens after the login event.
Related reading: AI fraud detection software: a practical guide →
Stop fraud before it costs you
CrossClassify is live in under 48 hours. No infrastructure changes, no rip-and-replace — it works alongside your existing stack from day one.